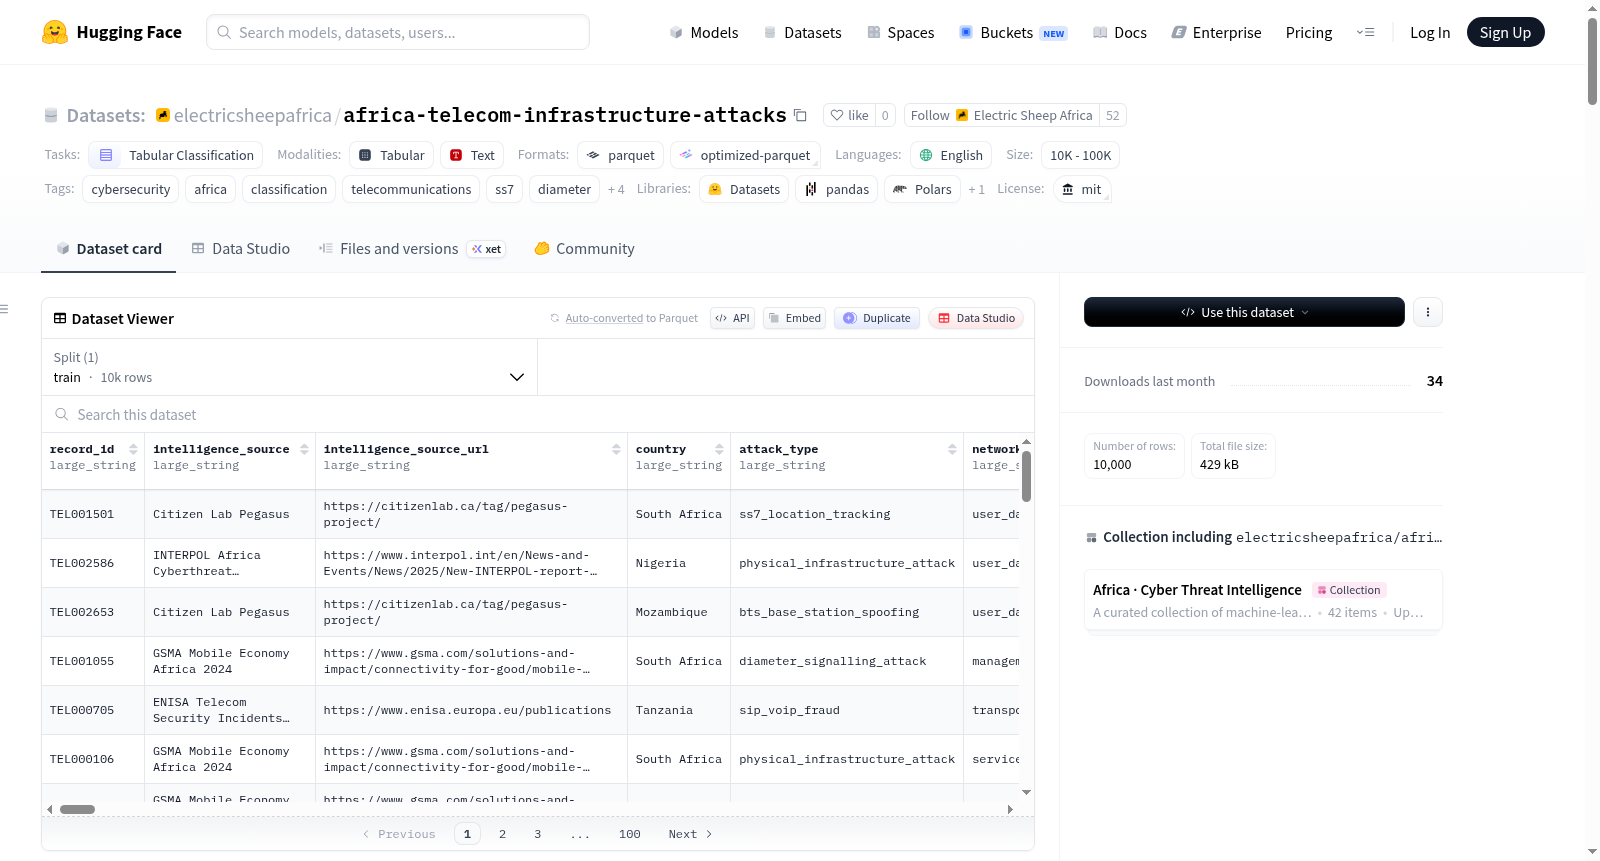
africa-telecom-infrastructure-attacks
收藏资源简介:
该数据集是一个合成的、平衡的表格分类数据集,专门用于建模和分析针对非洲电信基础设施的网络攻击。它包含10,000条记录(50%为攻击,50%为正常),所有记录均为合成数据。其核心目标是捕捉非洲移动优先环境(拥有6.15亿用户)中独特的电信安全威胁,这些威胁因安全投资不足(例如,少于30%的非洲移动网络运营商部署信令防火墙)和传统2G/3G网络(存在已知SS7漏洞)占主导地位而加剧。数据内容广泛覆盖了多种攻击类型,包括SIM交换欺诈、Diameter信令攻击、GTP隧道利用、SS7位置跟踪/呼叫短信拦截、IMSI捕获器监控、SIP/VoIP欺诈、BTS基站欺骗、5G NRF/SEPP利用、DNS/BGP劫持、海底电缆中断、核心网络入侵、CDR计费欺诈、OTA SIM攻击、合法监听滥用、物理基础设施攻击(如塔楼破坏、电缆/柴油盗窃)以及移动货币平台攻击等。数据集模拟了跨越2G到5G的多种协议(如SS7 MAP/ISUP/CAP、Diameter S6a/Gx/Rx、GTP、SIP、PFCP、HTTP/2 SBI)以及关键的运输层和服务层基础设施(如BGP/DNS、移动货币API)。特别强调了非洲特有的攻击模式和背景,例如南非的SIM交换流行病、尼日利亚的SIM注册欺诈和BTS欺骗、肯尼亚通过SIM交换针对M-Pesa的金融盗窃、埃及作为监控瓶颈的电信网络,以及将SIM交换与移动货币访问相结合的独特非洲攻击链。还考虑了区域性风险因素,如广泛使用的中国供应商(华为/中兴)核心网络设备、对海底电缆(如WACS、SAT-3、EASSy)的依赖(构成单点故障),以及物理盗窃和破坏等现实威胁。每条数据记录包含63个特征字段,详细描述了攻击的属性、影响和响应情况,关键字段包括攻击类型、目标国家、利用的协议、威胁行为者类型、所需访问级别、是否利用传统协议/Diameter/5G协议、是否涉及中国设备、SIM交换的具体方法、是否以移动货币或监控为目标、受影响用户和服务的规模指标、财务损失、物理破坏指标、检测与响应措施以及最终的二元分类标签(攻击或正常)。数据集还包含衍生特征,用于计算威胁评分、风险评分和生成各类别的一热编码。它适用于电信网络安全、威胁情报分析、攻击检测模型开发(分类任务)以及研究非洲特定网络威胁格局等任务。数据基于GSMA、ENISA、INTERPOL、Citizen Lab和AdaptiveMobile Security等机构的真实世界研究和报告生成,旨在为学术研究和安全工具开发提供高质量的合成基准数据。
This is a synthetic, balanced tabular classification dataset specifically designed for modeling and analyzing cyberattacks targeting African telecommunications infrastructure. It contains 10,000 records (50% attack samples, 50% normal samples), with all data being synthetically generated. Its core objective is to capture the unique telecommunications security threats in Africa's mobile-first environment (with 615 million users), which are exacerbated by insufficient security investment (e.g., fewer than 30% of African mobile network operators deploy signaling firewalls) and the dominance of legacy 2G/3G networks with known SS7 vulnerabilities. The dataset covers a wide range of attack types, including SIM swap fraud, Diameter signaling attacks, GTP tunnel exploitation, SS7 location tracking/call/SMS interception, IMSI catcher surveillance, SIP/VoIP fraud, BTS base station spoofing, 5G NRF/SEPP exploitation, DNS/BGP hijacking, submarine cable disruption, core network intrusion, CDR billing fraud, OTA SIM attacks, lawful interception abuse, physical infrastructure attacks (e.g., tower sabotage, cable/diesel theft) and mobile money platform attacks. It simulates multiple protocols spanning 2G to 5G (e.g., SS7 MAP/ISUP/CAP, Diameter S6a/Gx/Rx, GTP, SIP, PFCP, HTTP/2 SBI) as well as critical transport and service layer infrastructures (e.g., BGP/DNS, mobile money APIs). The dataset specifically highlights Africa-specific attack patterns and contexts, such as the SIM swap epidemic in South Africa, SIM registration fraud and BTS spoofing in Nigeria, financial theft targeting M-Pesa via SIM swapping in Kenya, telecommunications networks in Egypt acting as surveillance bottlenecks, and unique African attack chains combining SIM swapping and mobile money access. It also accounts for regional risk factors, such as the widespread use of core network equipment from Chinese vendors (Huawei/ZTE), reliance on submarine cables (e.g., WACS, SAT-3, EASSy) which create single points of failure, and real-world threats like physical theft and sabotage. Each data record contains 63 feature fields that comprehensively describe the attributes, impacts and responses of attacks. Key fields include attack type, target country, exploited protocol, threat actor type, required access level, whether legacy/Diameter/5G protocols are exploited, whether Chinese equipment is involved, specific SIM swap methods, whether the attack targets mobile money or surveillance, scale metrics of affected users and services, financial losses, physical damage metrics, detection and response measures, and the final binary classification label (attack or normal). The dataset also includes derived features for calculating threat scores, risk scores and generating one-hot encodings for various categories. It is applicable to tasks such as telecommunications network security, threat intelligence analysis, attack detection model development (classification tasks) and research on Africa-specific cyber threat landscapes. The dataset is generated based on real-world research and reports from organizations including GSMA, ENISA, INTERPOL, Citizen Lab and AdaptiveMobile Security, aiming to provide high-quality synthetic benchmark data for academic research and security tool development.
数据集概述:非洲电信基础设施攻击(超越 SS7)
该数据集属于 Africa Cyber Threat Intelligence 系列,由 electricsheepafrica 提供,专注于模拟非洲电信基础设施面临的各类攻击威胁。
基本信息
- 数据集名称:Telecommunications Infrastructure Attacks (Beyond SS7) — Africa Cyber Threat Intelligence
- 语言:英语
- 许可证:MIT
- 任务类型:表格分类(tabular-classification)
- 数据规模:10,000 行(平衡数据集,正负样本各 50%)
- 数据性质:全部为合成数据(is_synthetic=1),基于真实世界研究数据生成
数据集背景与地域特征
数据聚焦非洲移动优先的电信环境,覆盖:
- 南非:Vodacom/MTN SIM 卡交换欺诈(年损失超 3 亿兰特)、Cell C 数据泄露、海底电缆依赖
- 尼日利亚:MTN Nigeria SIM 注册欺诈、NCC 监管漏洞、拉各斯 BTS 伪基站攻击
- 肯尼亚:Safaricom M-Pesa SIM 换卡导致金融盗窃、IMSI 捕获器监控报告
- 埃及:Telecom Egypt 监控瓶颈、亚历山大港电缆着陆点风险
- 全非洲通用:SIM 换卡 → 移动货币访问 → 金融盗窃(独特攻击链)
攻击类型(共 19 类)
| 攻击类型 | 说明 |
|---|---|
| sim_swap_fraud | SIM 换卡用于移动货币/银行盗窃 |
| diameter_signalling_attack | 4G/LTE Diameter 协议利用 |
| gtp_tunnel_exploitation | GTP 隧道攻击 |
| ss7_location_tracking | SS7 用户位置追踪 |
| ss7_call_sms_intercept | SS7 通话/SMS 拦截 |
| imsi_catcher_surveillance | 伪基站监控 |
| sip_voip_fraud | SIP/VoIP 话费欺诈 |
| bts_base_station_spoofing | 流氓基站攻击 |
| 5g_nrf_exploitation | 5G 网络存储功能攻击 |
| 5g_sepp_bypass | 5G 安全边缘保护代理绕过 |
| dns_hijacking_telecom | 电信基础设施 DNS 劫持 |
| bgp_hijacking | BGP 路由劫持 |
| submarine_cable_disruption | 海底电缆攻击/切断 |
| core_network_intrusion | 核心网络入侵 |
| cdrs_billing_fraud | CDR 操纵/计费欺诈 |
| ota_sim_attack | 空中 SIM 工具包攻击 |
| lawful_intercept_abuse | 合法拦截能力滥用 |
| physical_infrastructure_attack | 铁塔/电缆/设备物理攻击 |
| mobile_money_platform_attack | 移动货币平台攻击 |
| roaming_fraud | 漫游互联欺诈 |
协议建模
| 协议 | 代际 | 说明 |
|---|---|---|
| SS7 MAP/ISUP/CAP | 2G/3G | 传统信令(非洲仍占主导) |
| Diameter S6a/Gx/Rx | 4G LTE | 随 LTE 扩展而增长的攻击面 |
| GTP v1/v2 | 3G/4G | GPRS 隧道协议 |
| SIP/RTP | 全代际 | IP 语音 |
| PFCP | 5G | 分组转发控制协议 |
| HTTP/2 SBI | 5G | 5G 服务化接口 |
| BGP/DNS | 传输层 | 路由和命名基础设施 |
| OTA SMS/USSD | 2G-4G | SIM 管理通道 |
| Mobile Money API | 服务层 | M-Pesa 等平台 |
海底电缆建模
WACS · SAT-3 · EASSy · SEACOM · 2Africa · MainOne · ACE · Equiano · PEACE
特征列说明(共 50+ 列)
| 类别 | 列名示例 |
|---|---|
| 基础信息 | record_id, country, attack_type, network_layer, protocol_exploited, threat_actor, target_operator, network_generation |
| 访问条件 | requires_network_access, requires_insider_access, requires_physical_access |
| 协议利用 | exploits_legacy_protocol, exploits_diameter, exploits_5g_protocol, exploits_vendor_backdoor |
| SIM 换卡 | sim_swap_social_engineering, sim_swap_insider_collusion, sim_swap_document_forgery, mobile_money_targeted |
| 监控相关 | surveillance_purpose, targets_journalist_activist, targets_political_figure, commercial_spyware_used |
| 影响规模 | subscribers_affected, calls_intercepted, sms_intercepted, locations_tracked |
| 经济损失 | financial_loss_usd, revenue_loss_per_hour_usd, fraud_revenue_usd |
| 物理攻击 | cable_cut, tower_vandalised, fibre_stolen, diesel_theft, submarine_cable_name |
| 检测与响应 | detected, time_to_detect_hours, detected_by, signalling_firewall_deployed, incident_response_activated, regulator_notified, gsma_reported, law_enforcement_involved, patch_applied |
| 标签 | label(1=攻击,0=合法) |
| 标记 | is_synthetic(全部为1) |
衍生特征
- 协议利用类:legacy_protocol, diameter_attack, fiveg_attack, beyond_ss7
- SIM 换卡链:is_sim_swap, sim_swap_mobile_money
- 监控类:surveillance_attack, authoritarian_surveillance, targets_civil_society
- 物理攻击类:physical_attack, submarine_cable_attack, infrastructure_theft
- 影响规模:mass_subscriber_impact, nationwide_impact
- 拦截类:interception_attack, mass_surveillance
- 财务影响:any_financial_loss, high_fraud
- 防御态势:has_signalling_firewall, effective_response
- 独热编码攻击类型(21 种):type_sim_swap, type_diameter, type_5g_nrf 等
- 代际标记:gen_2g, gen_4g, gen_5g, gen_legacy
- 行为者类型:actor_state, actor_sim_swap_gang, actor_surveillance_vendor
- 区域标记:is_west_africa, high_mobile_country
- 综合评分:telecom_threat_score, surveillance_risk_score, infrastructure_resilience_score
数据来源
- GSMA Mobile Economy Africa 2024
- ENISA Telecom Security Incidents Report 2024
- Europol/INTERPOL SIM-swapping reports 2024-2025
- GSMA FS.11 SS7/Diameter Security Guidelines 2024
- 3GPP 5G Security Architecture (TS 33.501)
- AdaptiveMobile Security — Simjacker & African MNO vulnerabilities
- Citizen Lab — Pegasus/surveillance via African telecom
- INTERPOL Africa Cyberthreat Assessment 2025