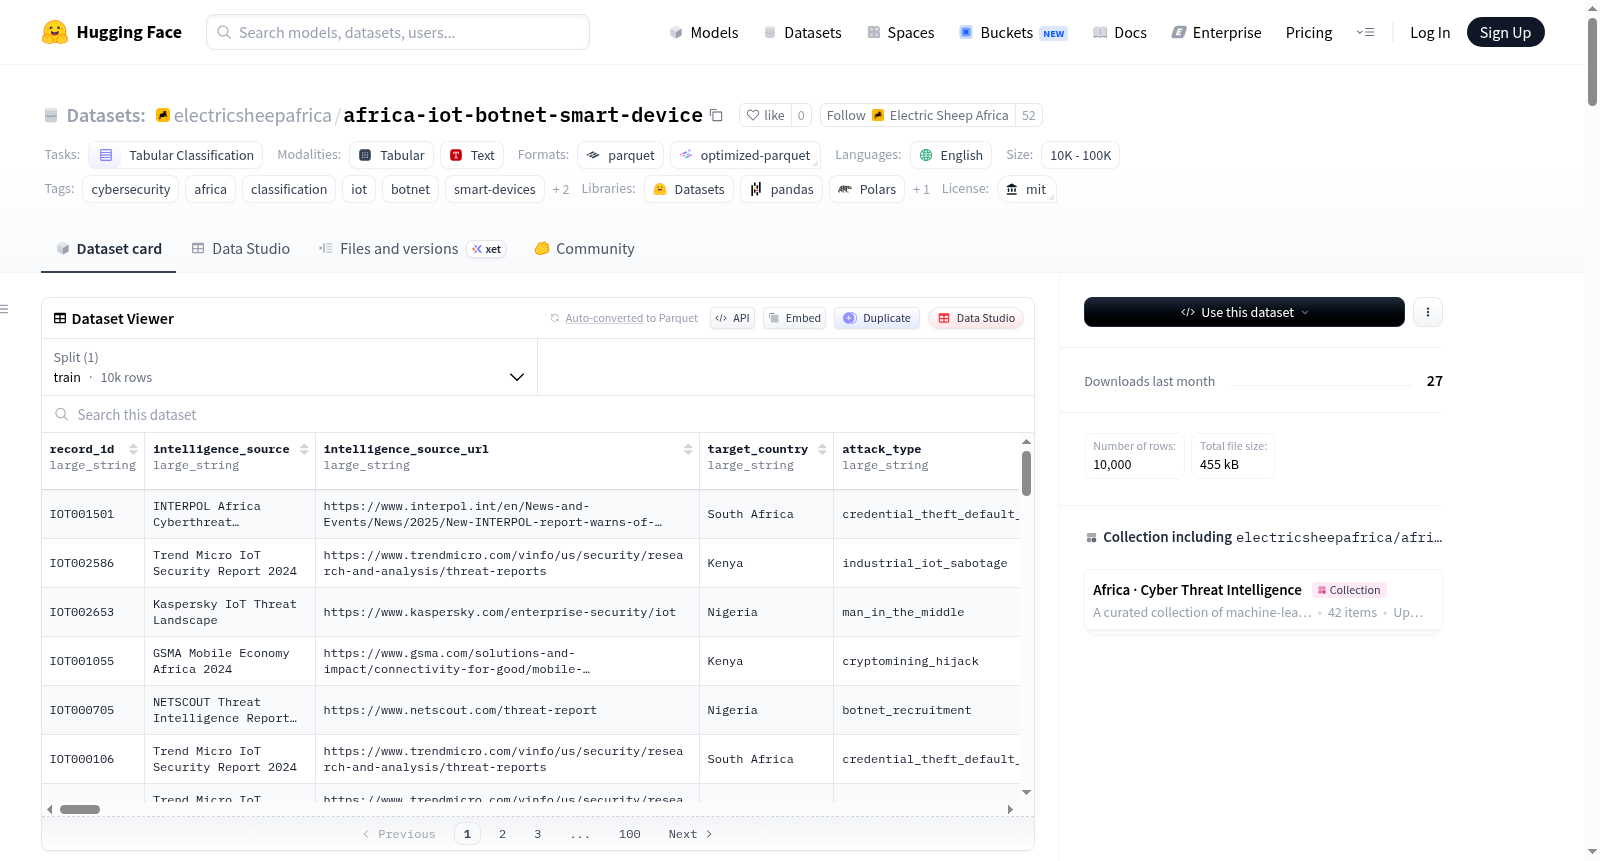
africa-iot-botnet-smart-device
收藏资源简介:
该数据集是一个合成的表格分类数据集,旨在模拟非洲地区的物联网(IoT)僵尸网络招募和智能设备攻击场景。它包含10,000条平衡记录(正负样本各50%),所有数据均为基于真实世界研究报告生成的合成数据。背景源于非洲严峻的物联网安全形势,该地区拥有超过7亿台联网设备但缺乏安全防护,使其成为全球物联网威胁攻击最多的地区之一。数据集特别捕捉了非洲不同国家的特定攻击模式,如南非的智能城市项目攻击、尼日利亚的ISP路由器入侵、肯尼亚的智慧农业传感器攻击和埃及的智能电网攻击等。数据内容涵盖多种攻击类型(如僵尸网络招募、DDoS攻击、加密劫持)、设备类型(如家庭路由器、智能电表、IP摄像头)和僵尸网络家族(如Mirai变种、Gafgyt)。数据集提供约50个特征字段,包括标识与基础信息、攻击与威胁特征、设备状态与配置、影响与损失指标、检测与响应指标以及衍生特征。它适用于物联网安全威胁检测、僵尸网络行为分析等表格分类任务,并参考了NETSCOUT、卡巴斯基等权威机构2024-2025年的威胁情报报告。
This dataset is a synthetic tabular classification dataset designed to simulate IoT botnet recruitment and smart device attack scenarios in Africa. It contains 10,000 balanced records (50% positive and negative samples each), with all data being synthetic and generated based on real-world research reports. The background stems from the severe IoT security situation in Africa, where over 700 million connected devices lack security protection, making it one of the regions with the highest global IoT threat attacks. The dataset specifically captures attack patterns from different African countries, such as smart city project attacks in South Africa, ISP router invasions in Nigeria, smart agriculture sensor attacks in Kenya, and smart grid attacks in Egypt. The data covers various attack types (e.g., botnet recruitment, DDoS attacks, cryptojacking), device types (e.g., home routers, smart meters, IP cameras), and botnet families (e.g., Mirai variants, Gafgyt). It provides approximately 50 feature fields, including identification and basic information, attack and threat characteristics, device status and configuration, impact and loss metrics, detection and response indicators, and derived features. The dataset is suitable for tabular classification tasks such as IoT security threat detection and botnet behavior analysis, and references threat intelligence reports from authoritative organizations like NETSCOUT and Kaspersky for 2024-2025.
数据集概述:IoT Botnet & Smart Device Attacks (Africa)
基本信息
- 数据集名称: IoT Botnet & Smart Device Attacks (Africa)
- 数据集主页: https://huggingface.co/datasets/electricsheepafrica/africa-iot-botnet-smart-device
- 语言: 英语
- 许可证: MIT
- 数据类型: 表格分类(tabular-classification)
- 数据规模: 10,000 行(平衡分布,50/50)
- 数据性质: 全部为合成数据(is_synthetic=1),基于真实研究数据生成
- 所属系列: Africa Cyber Threat Intelligence
数据集背景
该数据集模拟非洲国家的物联网僵尸网络招募和智能设备攻击场景。非洲拥有超过 7 亿台连接设备,但安全防护薄弱,是全球物联网威胁最严重的地区。非洲 IP 空间贡献了全球 14% 的 DDoS 僵尸网络流量,市场上充斥着使用默认凭证且缺乏更新机制的廉价中国制造设备。
针对非洲的特定模式
- 南非: 智慧城市项目、矿业 SCADA/ICS、预付费电表破解
- 尼日利亚: ISP CPE 路由器大规模入侵、家用路由器 Mirai 变种感染
- 肯尼亚: 智慧农业 IoT 传感器、M-Pesa POS 终端攻击、太阳能逆变器攻击
- 埃及: 智能电网部署、苏伊士工业 IoT
- 非洲大陆: 7 亿+设备,多数为不安全的中国通用设备,默认开放 telnet/SSH
- 独特威胁: 智能预付费电表操控窃电、太阳能逆变器僵尸网络招募
- 检测缺口: 大多数非洲 ISP 缺乏 IoT 威胁监控能力
攻击类型(12 种)
| 攻击类型 | 描述 |
|---|---|
| botnet_recruitment | 将设备招募进僵尸网络 |
| ddos_attack | 利用受感染设备发起 DDoS |
| cryptomining_hijack | 劫持设备 CPU 进行加密货币挖矿 |
| data_exfiltration | 从 IoT 设备窃取数据 |
| credential_theft_default_pass | 利用默认密码进行攻击 |
| firmware_exploitation | 利用固件漏洞进行攻击 |
| man_in_the_middle | 拦截 IoT 通信 |
| ransomware_iot | 针对 IoT/OT 的勒索软件 |
| smart_meter_manipulation | 篡改公用事业电表 |
| camera_surveillance_hijack | 劫持监控摄像头 |
| industrial_iot_sabotage | 攻击工业控制系统 |
| lateral_movement_pivot | 将 IoT 作为网络跳板 |
设备类型(12 种)
| 设备类型 | 非洲背景 |
|---|---|
| home_router | ISP 提供的 CPE,常未打补丁 |
| isp_cpe_modem | 大规模部署,使用默认凭证 |
| smart_prepaid_meter | 预付费电表,窃电目标 |
| solar_inverter_controller | 离网太阳能 IoT,快速增长 |
| ip_camera / dvr_nvr | 中国海康威视/大华,默认密码 |
| agricultural_sensor | 智慧农业,可进入农场网络 |
| pos_terminal | M-Pesa/支付终端 |
| industrial_plc_scada | 矿业和能源 SCADA |
| smart_water_meter | 市政水务 IoT |
| vehicle_tracking_device | 车队管理 IoT |
| smart_streetlight | 智慧城市基础设施 |
僵尸网络家族(6 种)
| 家族 | 描述 |
|---|---|
| Mirai_variant | 主导 IoT 僵尸网络,多个针对非洲的变种 |
| Manga_Dark_Mirai | 针对非洲路由器的 Mirai 分支 |
| Gafgyt_Bashlite | 第二常见的 IoT 僵尸网络 |
| Mozi | 针对路由器的 P2P 僵尸网络 |
| BotenaGo | 利用 30+ 漏洞 |
| custom_african_botnet | 本地开发的僵尸网络 |
数据特征(44 个原始列 + 衍生特征)
原始特征示例
- 标识: record_id(唯一标识符)
- 地理信息: target_country(20 个非洲国家)
- 攻击信息: attack_type、botnet_family、device_type、device_manufacturer、vulnerability_exploited
- 设备状态: firmware_outdated、default_credentials_used、device_has_update_mechanism、device_age_months、exposed_to_internet
- 网络安全: open_telnet、open_ssh、no_firewall、flat_network、uses_upnp
- 僵尸网络特征: part_of_botnet、botnet_size_estimate、c2_communication_encrypted、c2_uses_dga、p2p_botnet
- 攻击影响: ddos_bandwidth_gbps、ddos_type、financial_loss_usd、electricity_theft、physical_safety_risk
- 检测与响应: detected、detected_by、time_to_detect_days、device_remediated、isp_involved
- 标签: label(1 = IoT 攻击,0 = 合法流量)、is_synthetic(始终为 1)
衍生特征示例
- 设备风险评估: device_vulnerability_score、critically_exposed、default_credentials
- 僵尸网络特征: is_botnet、large_botnet、advanced_c2
- DDoS 指标: is_ddos、high_bandwidth_ddos、massive_ddos
- 影响评分: impact_score、electricity_theft、physical_safety_risk
- 检测能力: was_detected、quick_detection、undetected
- 复合评分: iot_threat_score、device_risk_score、detection_gap_score
情报来源
该数据集基于以下真实世界的威胁情报研究生成:
- NETSCOUT Threat Intelligence Report 2024
- Kaspersky IoT Threat Landscape 2024
- Nokia Threat Intelligence Report 2024
- Cloudflare DDoS Threat Report 2024
- INTERPOL Africa Cyberthreat Assessment 2025
- Spamhaus Botnet Threat Report 2024
- Trend Micro IoT Security Report 2024
- GSMA Mobile Economy Africa 2024
- Africa IoT/M2M Market Report 2024
引用格式
bibtex @misc{electricsheepafrica2026iotbotnet, title = {IoT Botnet & Smart Device Attacks (Africa)}, author = {Electric Sheep Africa}, year = {2026}, howpublished = {url{https://huggingface.co/datasets/electricsheepafrica/africa-iot-botnet-smart-device}} }