hookprobe/edge-ids-threats
收藏资源简介:
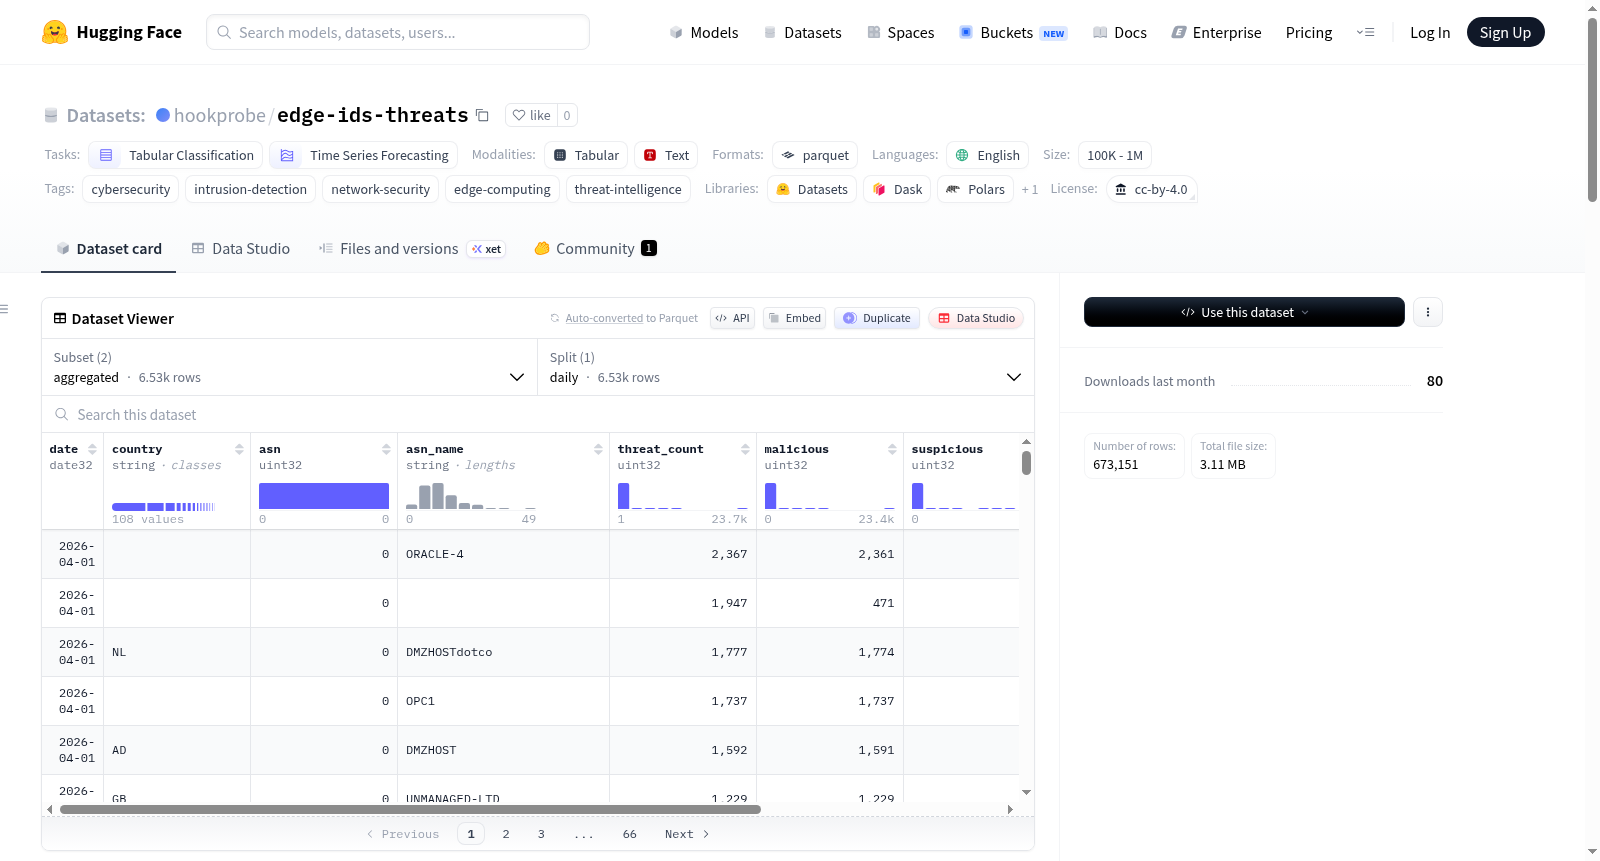
HookProbe Edge IDS Threat Telemetry数据集是一个真实世界的匿名威胁判定数据集,来自HookProbe生产边缘入侵检测系统。与合成实验室数据集(如CICIDS2017、UNSW-NB15、Kitsune)不同,这些数据是实际边缘传感器网格在开放互联网上观察到的,并由SENTINEL集合(隔离森林+校准朴素贝叶斯)标记。数据集包含两个主要配置:verdicts(主要数据)和aggregated(派生数据)。verdicts配置包含时间戳、源IP哈希、国家、ASN、异常分数、判定结果和采取的行动等字段。aggregated配置包含按国家/ASN/日聚合的威胁计数和平均异常分数。数据集还详细说明了隐私模型(如IP哈希和时间戳截断)、数据注意事项(如SENTINEL校准窗口的排除和地理/ASN分布的偏差)、引用信息、示例用法、更新频率和联系方式。
The HookProbe Edge IDS Threat Telemetry dataset is a real-world, anonymised threat verdict dataset from the HookProbe production edge intrusion-detection system. Unlike synthetic lab datasets (e.g., CICIDS2017, UNSW-NB15, Kitsune), this data represents what an actual edge sensor mesh observes on the open internet, labeled by the SENTINEL ensemble (isolation forest + calibrated naive-Bayes). The dataset includes two main configurations: verdicts (primary data) and aggregated (derived data). The verdicts configuration contains fields such as timestamp, source IP hash, country, ASN, anomaly score, verdict, and action taken. The aggregated configuration includes threat counts and average anomaly scores aggregated by country/ASN/day. The README also details the privacy model (e.g., IP hashing and timestamp truncation), data caveats (e.g., exclusion of the SENTINEL calibration window and skew in geographic/ASN distributions), citation information, example usage, update frequency, and contact details.