jniecko/ebpf-k8s-attack-detection
收藏资源简介:
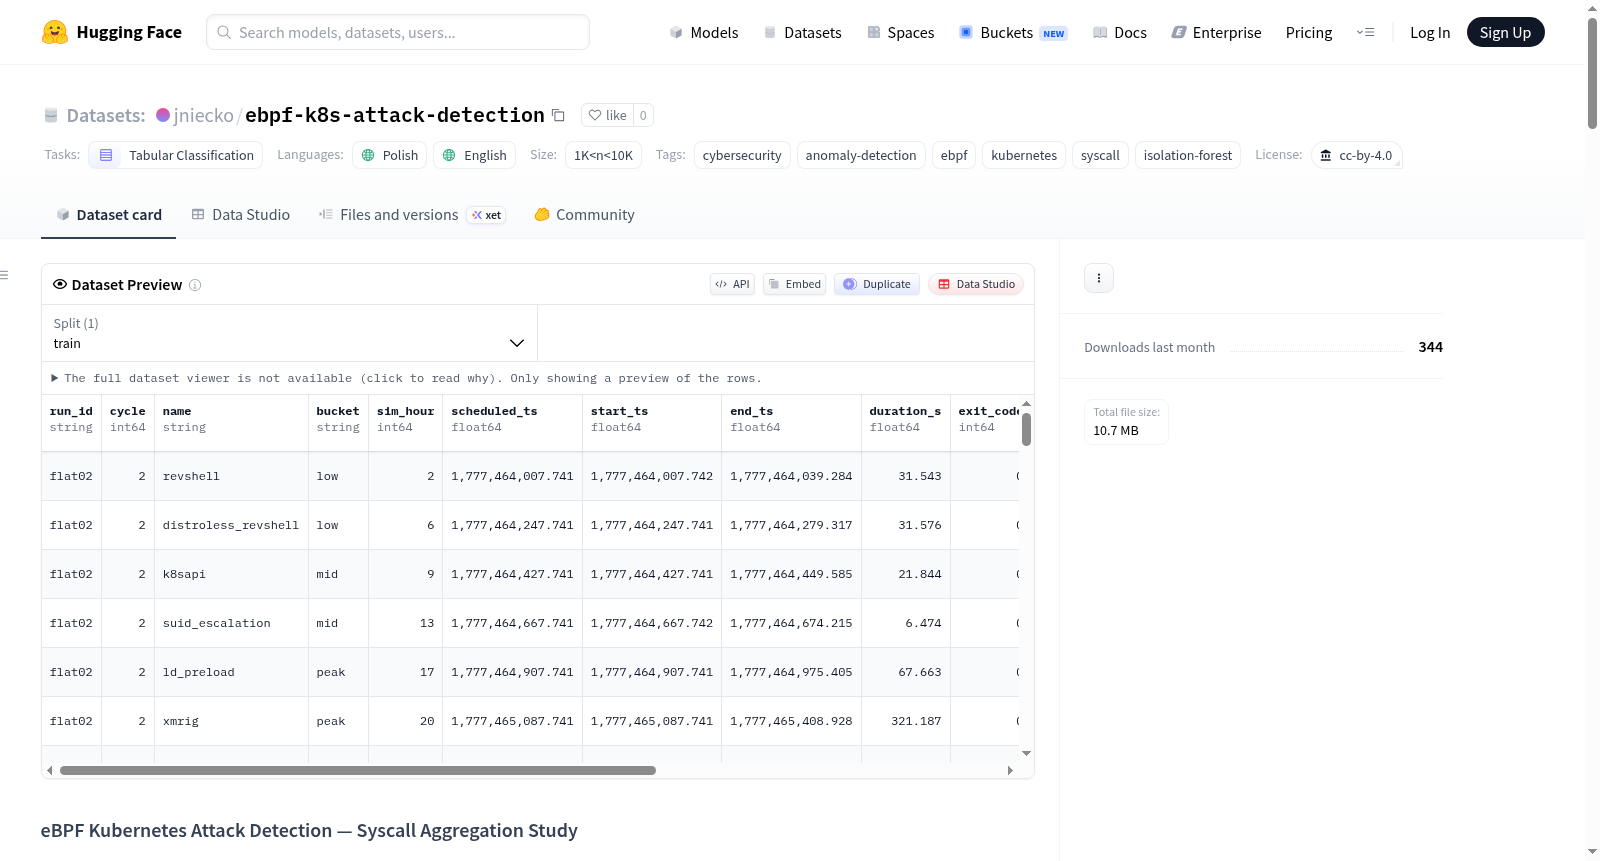
该数据集名为eBPF Kubernetes攻击检测——系统调用聚合研究,主要用于网络安全和异常检测领域。数据集基于在4节点Kubernetes集群(Kubernetes 1.35.4,Proxmox虚拟机,Intel Core i7-8700,32 GB RAM)上运行的Online Boutique微服务应用(11个服务)进行的两次实验运行。通过Tracee 0.24收集了21种内核事件类型的数据,包括系统调用计数和熵等特征。数据集包含两种流量配置文件:季节性负载(20-200虚拟用户)和恒定负载(100虚拟用户)。每种配置下都进行了训练和攻击阶段,共18次攻击实例(6种攻击类型×3次攻击周期)。攻击类型包括加密货币挖矿(xmrig)、反向shell(revshell)、无发行版容器中的反向shell(distroless_revshell)、Kubernetes API滥用(k8sapi)、通过SUID二进制文件提权(suid_escalation)和通过LD_PRELOAD环境变量进行共享库注入(ld_preload)。数据集还提供了详细的特征模式、实验结果和重现步骤。
The dataset is named eBPF Kubernetes Attack Detection — Syscall Aggregation Study and is primarily used in the fields of cybersecurity and anomaly detection. It is based on two experimental runs conducted on a 4-node Kubernetes cluster (Kubernetes 1.35.4, Proxmox VMs, Intel Core i7-8700, 32 GB RAM) running the Online Boutique microservices application (11 services). Kernel events were collected using Tracee 0.24, encompassing 21 event types, including syscall counts and entropy features. The dataset includes two traffic profiles: seasonal load (20-200 virtual users) and flat load (100 virtual users). Each profile consists of training and attack phases, with a total of 18 attack instances (6 attack types × 3 attack cycles). The attack types include cryptominer (xmrig), reverse shell (revshell), reverse shell in a distroless container (distroless_revshell), Kubernetes API abuse (k8sapi), privilege escalation via SUID binary (suid_escalation), and shared library injection via LD_PRELOAD environment variable (ld_preload). The dataset also provides detailed feature schemas, experimental results, and reproduction steps.