africa-ransomware-as-a-service
收藏资源简介:
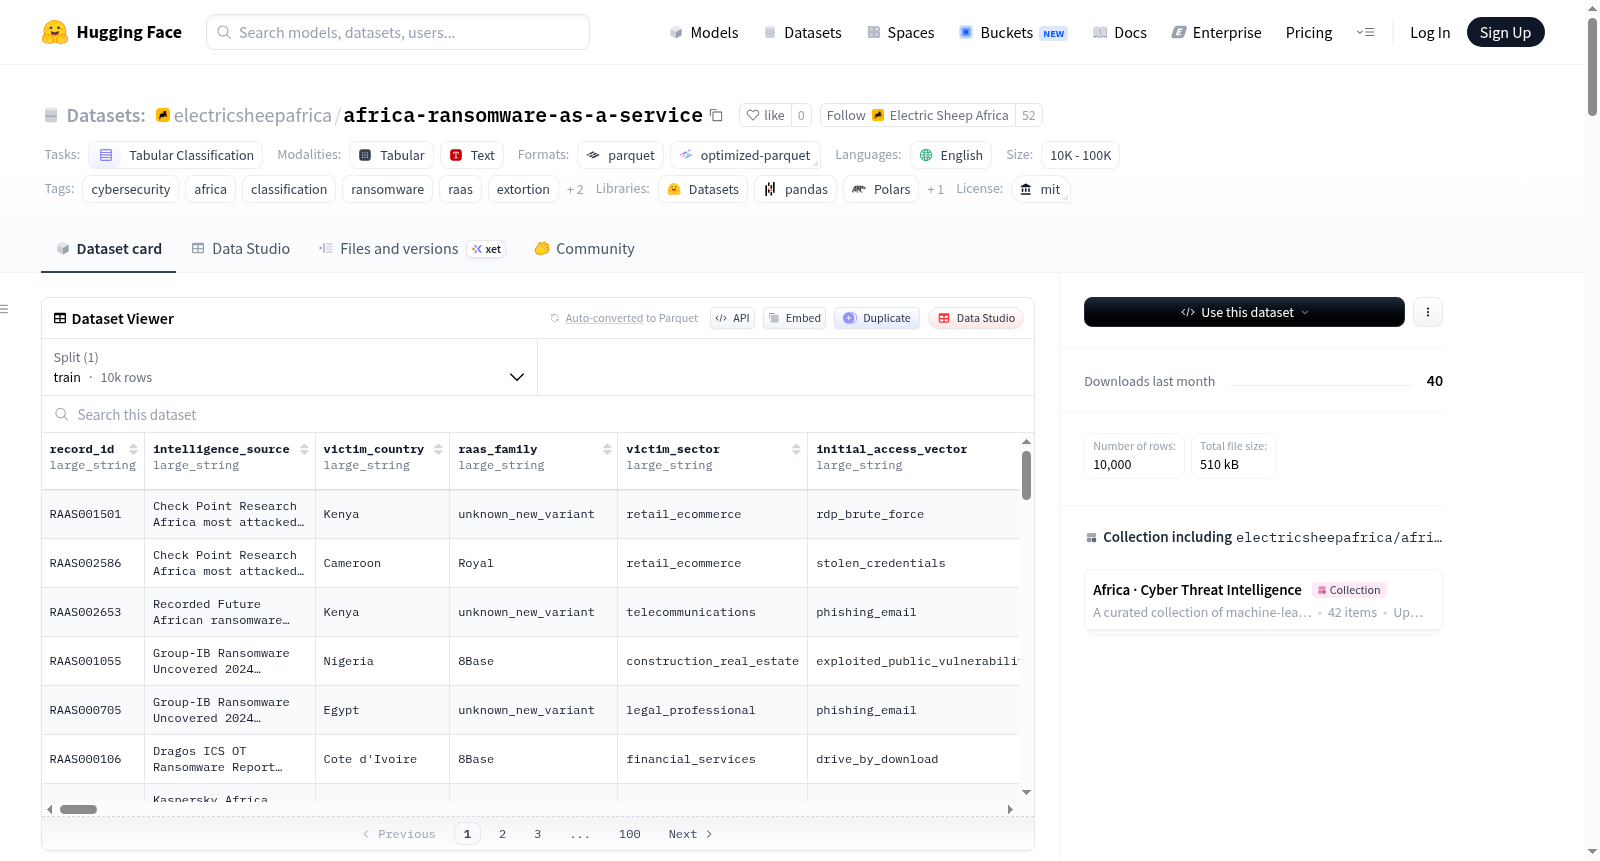
该数据集是一个合成的表格分类数据集,专注于模拟针对非洲组织的勒索软件即服务(RaaS)攻击,属于非洲网络威胁情报系列的一部分。它旨在反映非洲作为新勒索软件变种全球部署前测试场的独特动态,原因包括当地安全态势较低、执法响应较弱以及攻击者采取以量取胜的策略。数据集包含10,000条平衡记录(50%攻击,50%正常),所有数据均为基于真实世界研究报告生成的合成数据。数据内容涵盖了20个非洲国家,模拟了包括LockBit 3.0、ALPHV/BlackCat、Akira等在内的10个主要RaaS家族的攻击活动,以及网络钓鱼、漏洞利用、RDP暴力破解等7种初始访问向量。数据集提供了55个特征字段,详细描述了攻击事件的技术细节(如驻留时间、横向移动、权限提升)、影响后果(如财务损失、数据泄露、服务中断)、组织响应(如事件响应、执法联系)和恢复情况(如备份有效性、恢复时间)。此外,还提取了多个复合特征,如攻击深度分数、勒索级别、测试场分数、非洲利用分数等,用于量化攻击的复杂性和地域特异性。该数据集适用于网络安全领域的威胁情报分析、勒索软件攻击检测与分类模型训练、以及针对非洲地区网络安全风险的研究。
This dataset is a synthetic tabular classification dataset focused on simulating ransomware-as-a-Service (RaaS) attacks targeting African organizations, and is part of the African Cyber Threat Intelligence series. It aims to reflect the unique dynamics of Africa acting as a testbed for new ransomware variants prior to their global deployment, driven by factors including weak local security posture, limited law enforcement response, and attackers' quantity-over-quality tactics. The dataset contains 10,000 balanced records (50% attack cases, 50% benign cases), with all data generated synthetically based on real-world research reports. It covers 20 African countries, simulating attack activities from 10 major RaaS families including LockBit 3.0, ALPHV/BlackCat, Akira, and others, as well as 7 initial access vectors such as phishing, exploit attacks, and RDP brute-force attacks. The dataset provides 55 feature fields detailing technical specifics of attack incidents (e.g., dwell time, lateral movement, privilege escalation), impact consequences (e.g., financial loss, data breach, service disruption), organizational responses (e.g., incident response, law enforcement liaison), and recovery status (e.g., backup effectiveness, recovery time). Additionally, multiple composite features are extracted, such as attack depth score, ransomware severity level, testbed score, African exploitation score, etc., to quantify attack complexity and geographic specificity. This dataset is suitable for threat intelligence analysis in the cybersecurity domain, training of ransomware attack detection and classification models, and research on cybersecurity risks in the African region.