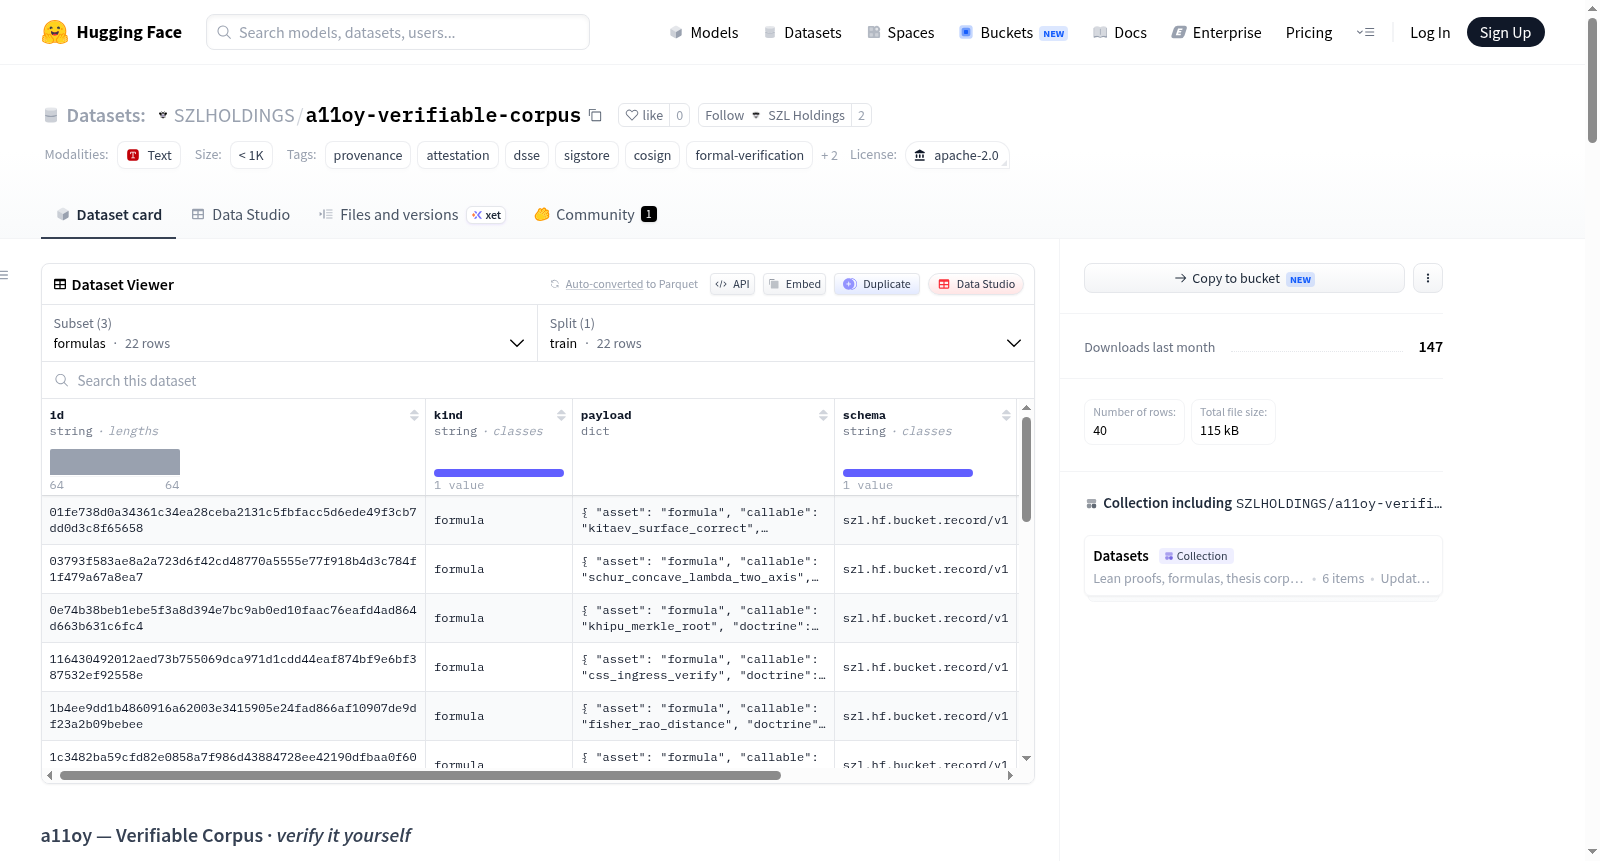
a11oy-verifiable-corpus
收藏资源简介:
a11oy可验证语料库是一个旨在提供完全可独立验证的数据集,遵循“无需信任,自行验证”的核心原则。它由SZL Holdings的a11oy系统生成,以仅追加、内容寻址的方式发布,确保历史记录的完整性和幂等性。数据集包含三个主要部分,均以NDJSON格式存储,并通过`head.json`文件维护链状态:1. 收据部分:包含完整的数字签名收据(DSSE信封)以及验证所需的所有密码学材料,支持两种真实的签名方案(ECDSA-P256-DSSE-PAE签名和Sigstore无密钥收据),并提供了详细的自行验证步骤和示例代码。2. 定理部分:嵌入了从lutar-lean仓库获取的、经Lean内核验证的定理列表,内容逐字节复制,每条记录包含原始Markdown文件内容、SHA256哈希、摘要(含计数和源文件自身声明的诚实标记)以及来源URL,用户可通过克隆源仓库并运行构建来独立验证。3. 公式部分:包含了a11oy规范公式注册表中的每个公式,记录包含公式名称、可调用函数及其证明状态,其中证明状态是从注册表中逐字复制的,反映了Lean内核和Doctrine v11诚实表面所定义的状态(如已证明、公理门控、假设、实数、猜想)。数据集遵循a11oy的诚实原则,明确区分条件性证明与无条件证明,并排除了所有非密码学签名的演示级工件。其数据规模较小(小于1K),适用于密码学证明、形式化验证、出处追溯、数字签名验证等任务,采用Apache-2.0许可证发布。
The a11oy Verifiable Corpus is a dataset designed to provide fully independently verifiable content, adhering to the core principle of "trust nothing, verify everything". It is generated by the a11oy system under SZL Holdings, and released in an append-only, content-addressable manner to ensure the integrity and idempotency of historical records. The dataset consists of three main components, all stored in NDJSON format, with the chain state maintained via the `head.json` file: 1. Receipts Component: Contains complete digitally signed receipts (DSSE envelopes) and all cryptographic materials required for verification, supporting two genuine signature schemes (ECDSA-P256-DSSE-PAE signatures and Sigstore keyless receipts), and provides detailed step-by-step self-verification instructions and sample code. 2. Theorems Component: Embeds a list of theorems verified by the Lean kernel, sourced from the lutar-lean repository with content copied byte-for-byte. Each record includes the original Markdown file content, SHA256 hash, metadata (including counts and the honesty marker declared by the source file itself), and the source URL. Users can independently verify by cloning the source repository and running the build process. 3. Formulas Component: Contains every formula from the a11oy canonical formula registry. Each record includes the formula name, callable functions, and its proof status. The proof status is copied verbatim from the registry, reflecting the state as defined by the Lean kernel and Doctrine v11's honest surface (e.g., proven, axiom-gated, assumed, real numbers, conjectured). The dataset adheres to the a11oy honesty principle, explicitly distinguishes between conditional and unconditional proofs, and excludes all non-cryptographically signed demo-level artifacts. It is small in scale (fewer than 1,000 entries), suitable for tasks such as cryptographic proof, formal verification, provenance tracking, and digital signature verification, and is released under the Apache-2.0 license.
数据集概述
a11oy Verifiable Corpus 是一个专注于可验证性的数据集,旨在让任何用户都能独立验证其内容,无需信任数据发布者。数据集包含加密签名的收据、内核验证的定理列表和公式注册表。
- 许可证: Apache-2.0
- 规模: 少于 1000 条记录 (n<1K)
- 标签: provenance, attestation, dsse, sigstore, cosign, formal-verification, lean4, verify-it-yourself
数据集结构与配置
数据集包含三个主要配置,分别对应不同的数据类型:
| 配置名称 | 数据文件路径 | 描述 |
|---|---|---|
receipts |
receipts/*.ndjson |
加密签名的 DSSE 收据及验证数据 |
theorems |
theorems/*.ndjson |
Lean 4 内核验证的定理列表(逐字复制) |
formulas |
formulas/*.ndjson |
公式注册表及其证明状态(逐字复制) |
每个配置的 *.ndjson 文件均按日期分割(如 receipts/2026-06-12.ndjson),并且每个配置都包含一个 head.json 文件,记录链状态(计数、最后一个 ID、分片信息)。
每条记录都是一个桶信封 (bucket envelope),格式如下:
json { "schema": "szl.hf.bucket.record/v1", "id": "<sha256>", "ts": "...", "source": "a11oy", "kind": "receipt|theorem|formula", "payload": { ... } }
记录 ID (id) 是基于 {source, kind, content} 的内容寻址,而非时间戳,这使得重新发布具有幂等性。
1. 收据 (receipts/)
收据包含两种签名方案,均为真实签名,不含未签名或占位信封:
签名方案 (payload.scheme) |
含义 | 签名方式 |
|---|---|---|
ecdsa-p256-dsse-pae |
a11oy Khipu 收据 | 使用 SZL Holdings 的 cosign 密钥,对 DSSE PAE 进行 ECDSA-P256-SHA256 签名 |
sigstore-keyless-dsse |
治理门禁收据 | 在 CI 环境中使用 Sigstore 无密钥 方式(Fulcio 证书 + Rekor 透明度日志)签名 |
每个收据的 payload.envelope 包含完整的 DSSE 信封,payload.verify 提供验证方法。
验证 ecdsa-p256-dsse-pae 收据:
-
重构 DSSE PAE (Pre-Authentication Encoding):
PAE = b"DSSEv1 " + len(payloadType) + b" " + payloadType + b" " + len(payload) + b" " + payload
其中
payload是envelope.payload经 Base64 解码后的内容。 -
获取公钥:公钥发布在
https://raw.githubusercontent.com/szl-holdings/.github/main/cosign.pub。 -
使用 ECDSA-P256 算法和 SHA256 哈希函数,对 PAE 进行签名验证。
-
公钥内容(可用于验证):
-----BEGIN PUBLIC KEY----- MFkwEwYHKoZIzj0CAQYIKoZIzj0DAQcDQgAE/Jlv9FnwJ13l4QIZpr4IbTBUtVZ2 i+O7Jai/s7xsdXvOjmZGYhd36VxNQQahTSjWoYpPrSNhXbt/n7lsgi61xA== -----END PUBLIC KEY-----
验证 sigstore-keyless-dsse 收据:
- 信封本身包含完整的 Sigstore 包(
envelope._sigstore.bundle),包括 Fulcio 证书链和 Rekor 包含证明。 - 使用
cosign工具进行验证: bash cosign verify-blob-attestation --bundle bundle.json --new-bundle-format --certificate-identity-regexp github.com/szl-holdings/.* --certificate-oidc-issuer https://token.actions.githubusercontent.com statement.json
2. 定理 (theorems/)
该部分包含从 lutar-lean 的 VERIFIED_THEOREMS.md 文件中逐字复制的、经内核验证的定理列表。
payload.markdown: 文件的逐字节内容。payload.content_sha256: 文件内容的 SHA256 哈希值,可用于交叉验证。payload.summary: 来源文件自身声明的计数和诚实性标记。payload.source_url: 定理来源的 URL。
这些定理由 Lean 内核检查,不包含任何 sorry。用户可以克隆 lutar-lean 仓库并自行运行构建进行验证。
3. 公式 (formulas/)
该部分包含 a11oy 标准注册表中的公式记录。每条记录包含:
payload.name/payload.callable: 公式名称及其运行时函数。payload.proof_status: 从注册表的PROOF_STATUS中逐字复制的证明状态。
证明状态反映了 Lean 内核和 Doctrine v11 的诚实性表面,包括 PROVEN(已证明)、AXIOM(公理约束)、SORRY(未证明)、REAL(真实)和 CONJECTURE(猜想)。
诚实性与范围
该数据集遵循 a11oy 的 v11 诚实性原则:
- 定理 U 是 REAL but CONDITIONAL (在特定假设下证明),不是无条件证明。
- 猜想 1 (无条件的 Λ-唯一性) 是 OPEN 状态,且在 A1–A5 公理下经机器检查为假(存在显式反例)。
- 数据集不包含任何演示级别的 HMAC 收据或未加密签名的哈希链工件,只包含可通过公钥或透明度日志验证的材料。
来源
- 生产者: szl-holdings/a11oy 仓库的
szl_corpus_publish.py脚本。 - 定理来源: szl-holdings/lutar-lean 仓库。
- 公钥: 发布在 szl-holdings/.github/cosign.pub 。
- 许可证: Apache-2.0。